Where I Currently Serve
Organisations & platforms
What I do
Four disciplines. One connected practice.
I connect product decisions to the cloud, delivery systems and controls that let them last.
- 01CloudSecure foundations, identity, platforms and observability for systems that need to stay available.→
- 02Product DevelopmentDigital products, AI-enabled workflows and customer experiences built from concept to release.→
- 03DevOpsRepeatable delivery, infrastructure as code, release confidence and durable operating practices.→
- 04ComplianceControls, privacy and evidence engineered into the systems—not bolted on before an audit.→
Projects, organised by the work that matters
A working portfolio of cloud foundations, shipped products, delivery platforms and compliance-ready systems.
GCP Zero-Trust Architecture with Cloud Armor
I designed and deployed a production-grade zero-trust security architecture on Google Cloud Platform — moving away from the legacy perimeter-security model and replacing it with identity-first, policy-driven access controls. Every access request is evaluated against identity context, device posture, and resource sensitivity before being granted.
DevSecOps CI/CD Pipeline with SAST, DAST & GKE Deployment
I built a fully automated, security-integrated CI/CD pipeline — from commit to production on GKE — with security scanning embedded at every stage, not bolted on at the end.
Cloud SIEM: GCP + Chronicle Security Operations
I designed and deployed a cloud-native SIEM environment using Google Chronicle — complete log ingestion pipeline, 14 custom YARA-L detection rules, automated incident triage, and a documented incident response playbook.
IntelliDoc: AI-Powered Document Intelligence Platform
I designed and built IntelliDoc — a B2B document intelligence platform for SMBs, legal firms, and enterprises. Upload contracts, policies, and documents; interact with them through natural language Q&A, expiry alerts, and conflict detection.
Expertise
My Career Journey
My Certifications & Credentials
Speaking & Workshops
AI Risk Consulting
LEAD AI Risk Management examination consulting session with the Lead AI Risk Manager at Stanbic IBTC HQ
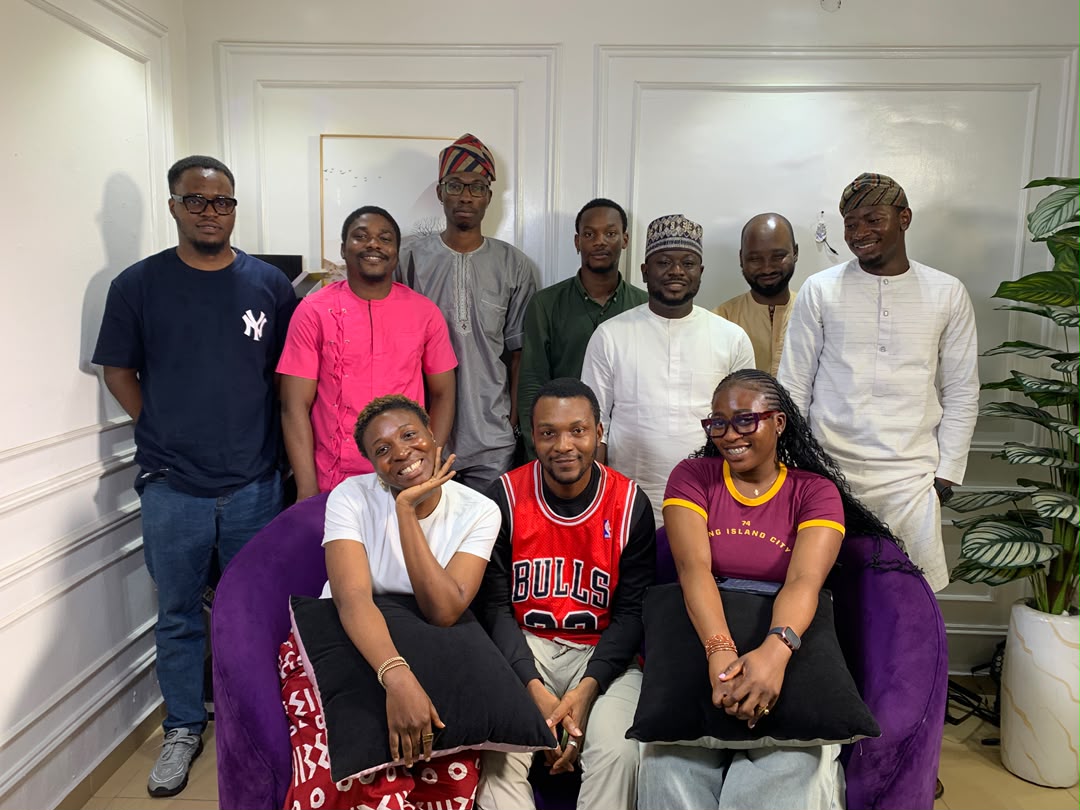
RHEL Consulting
With members of the Infrastructure team from LIRS and Stanbic IBTC after an educative consulting session on RHEL
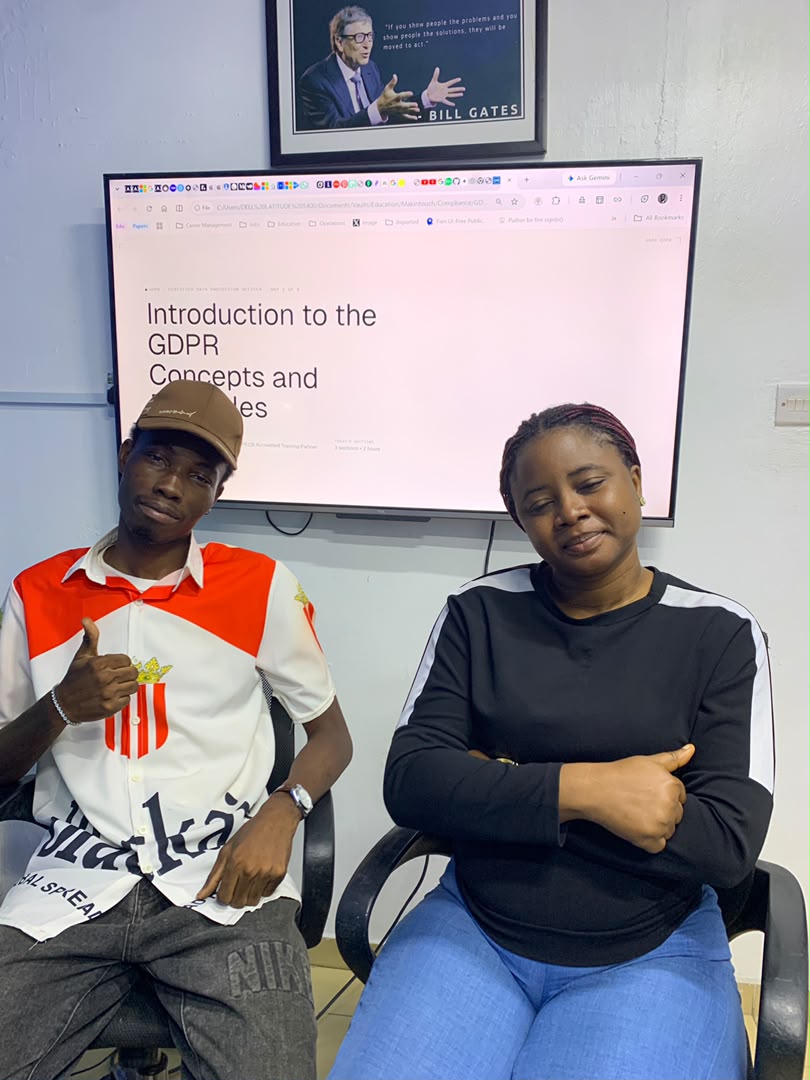
GDPR Consulting
With the DPO at Stanbic IBTC after a GDPR educative consulting session
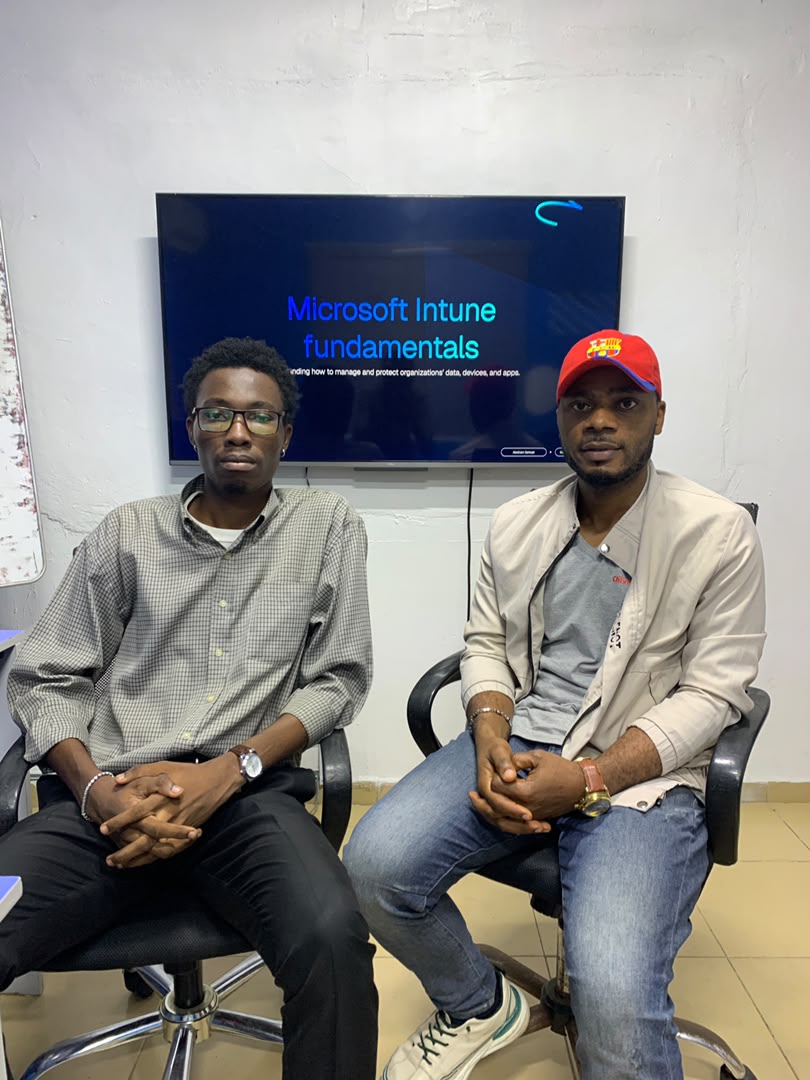
Microsoft Intune Session
Educative consulting session on Microsoft Intune fundamentals with a System Support Engineer at Chivita, Lagos
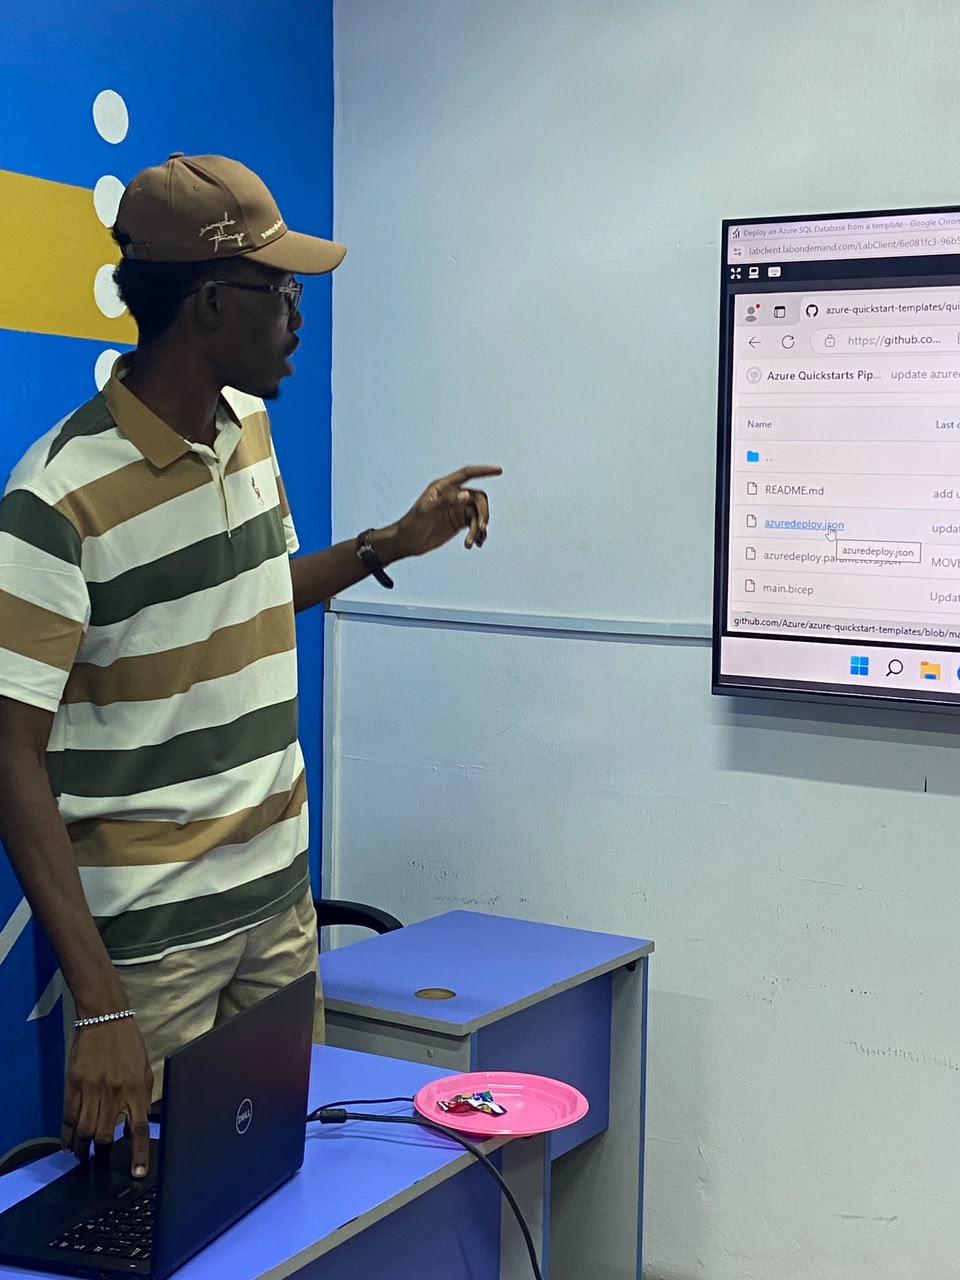
Server Management Consulting
Educative consulting session with staff from AMCON and Stanbic IBTC on Microsoft Server management
Keynote Speaking
Abraham O. Samuel speaking at a workshop
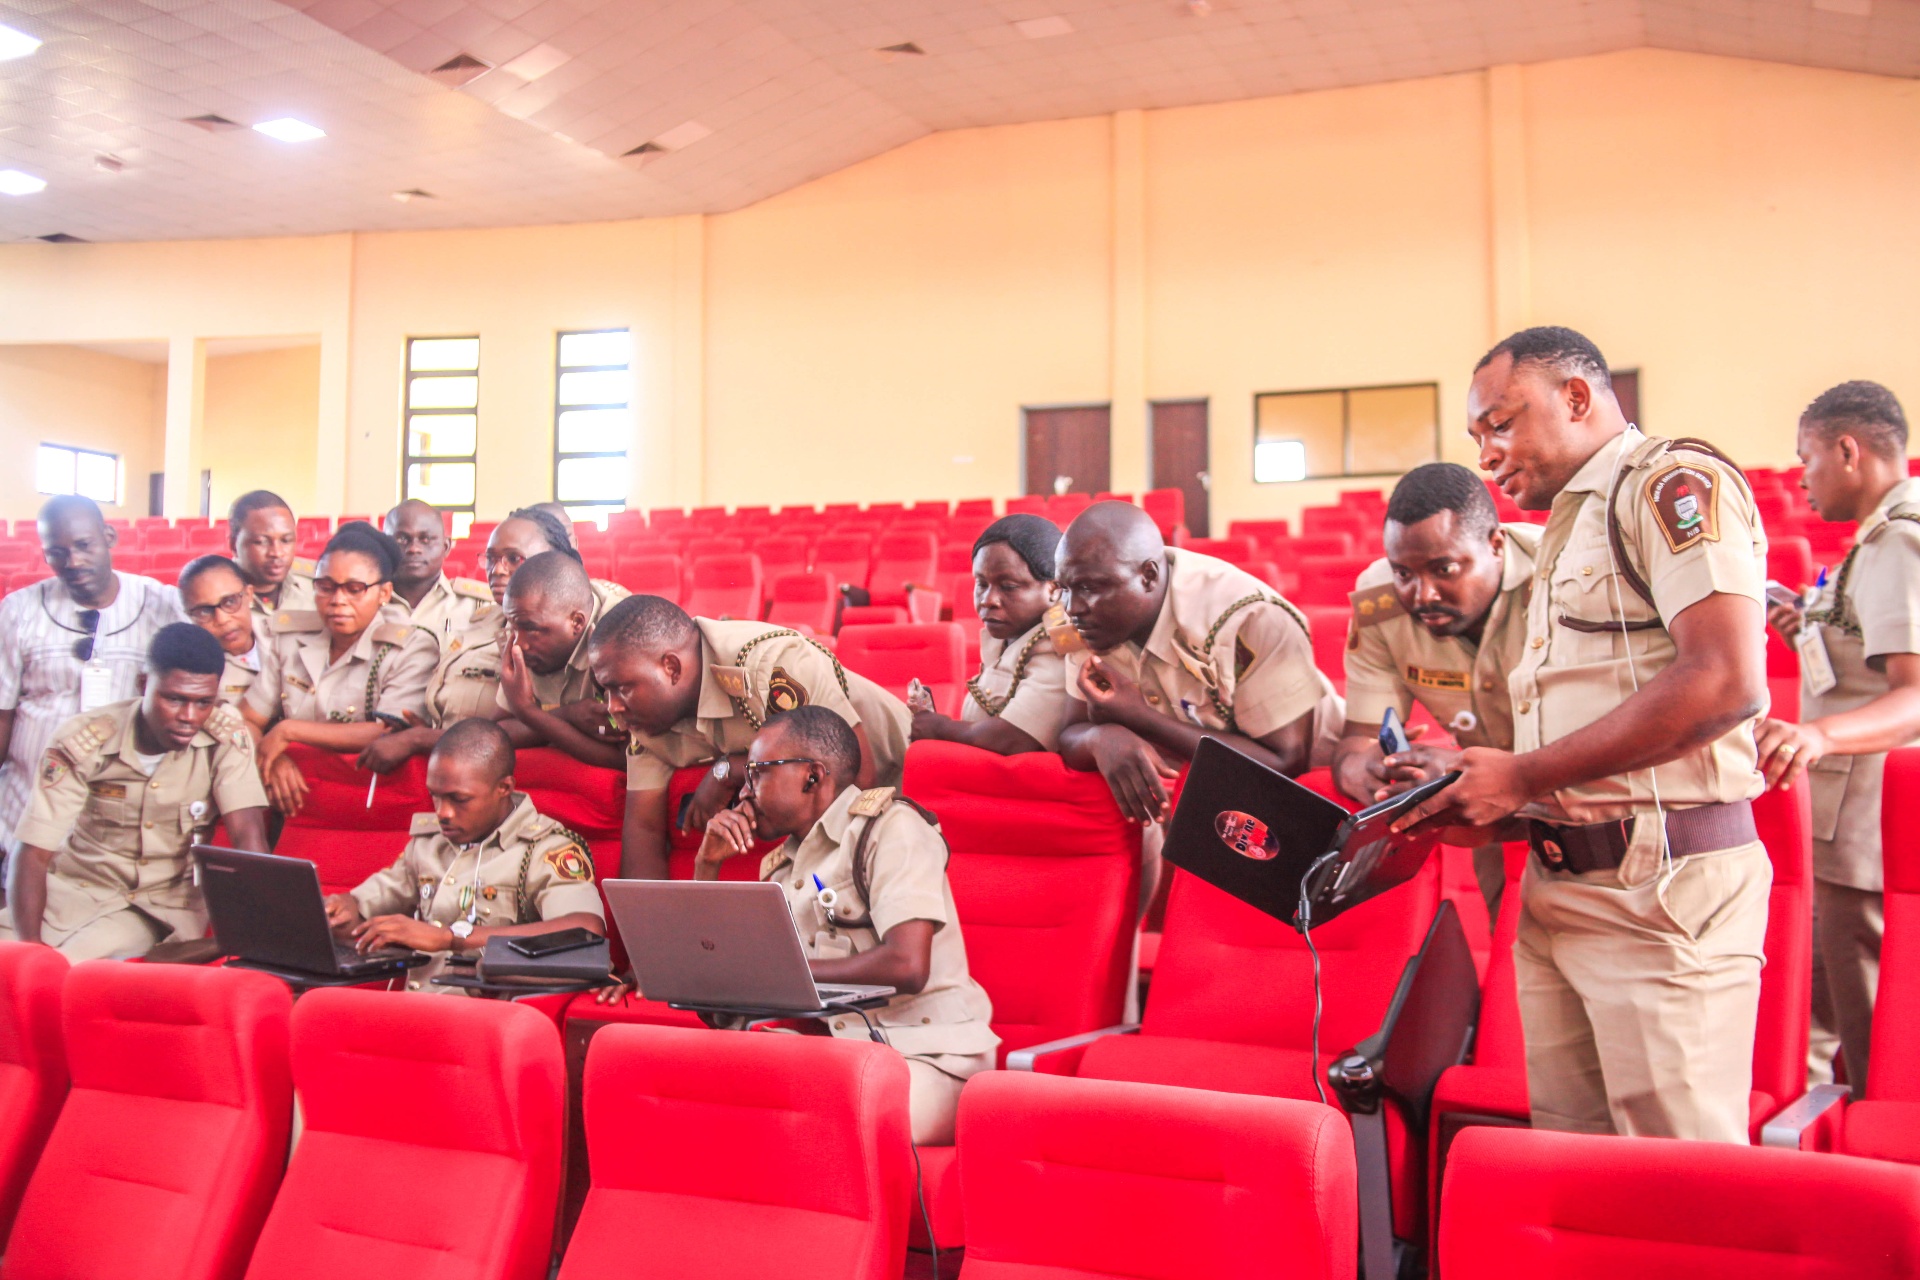
Hands-on Training
Workshop training session with participants
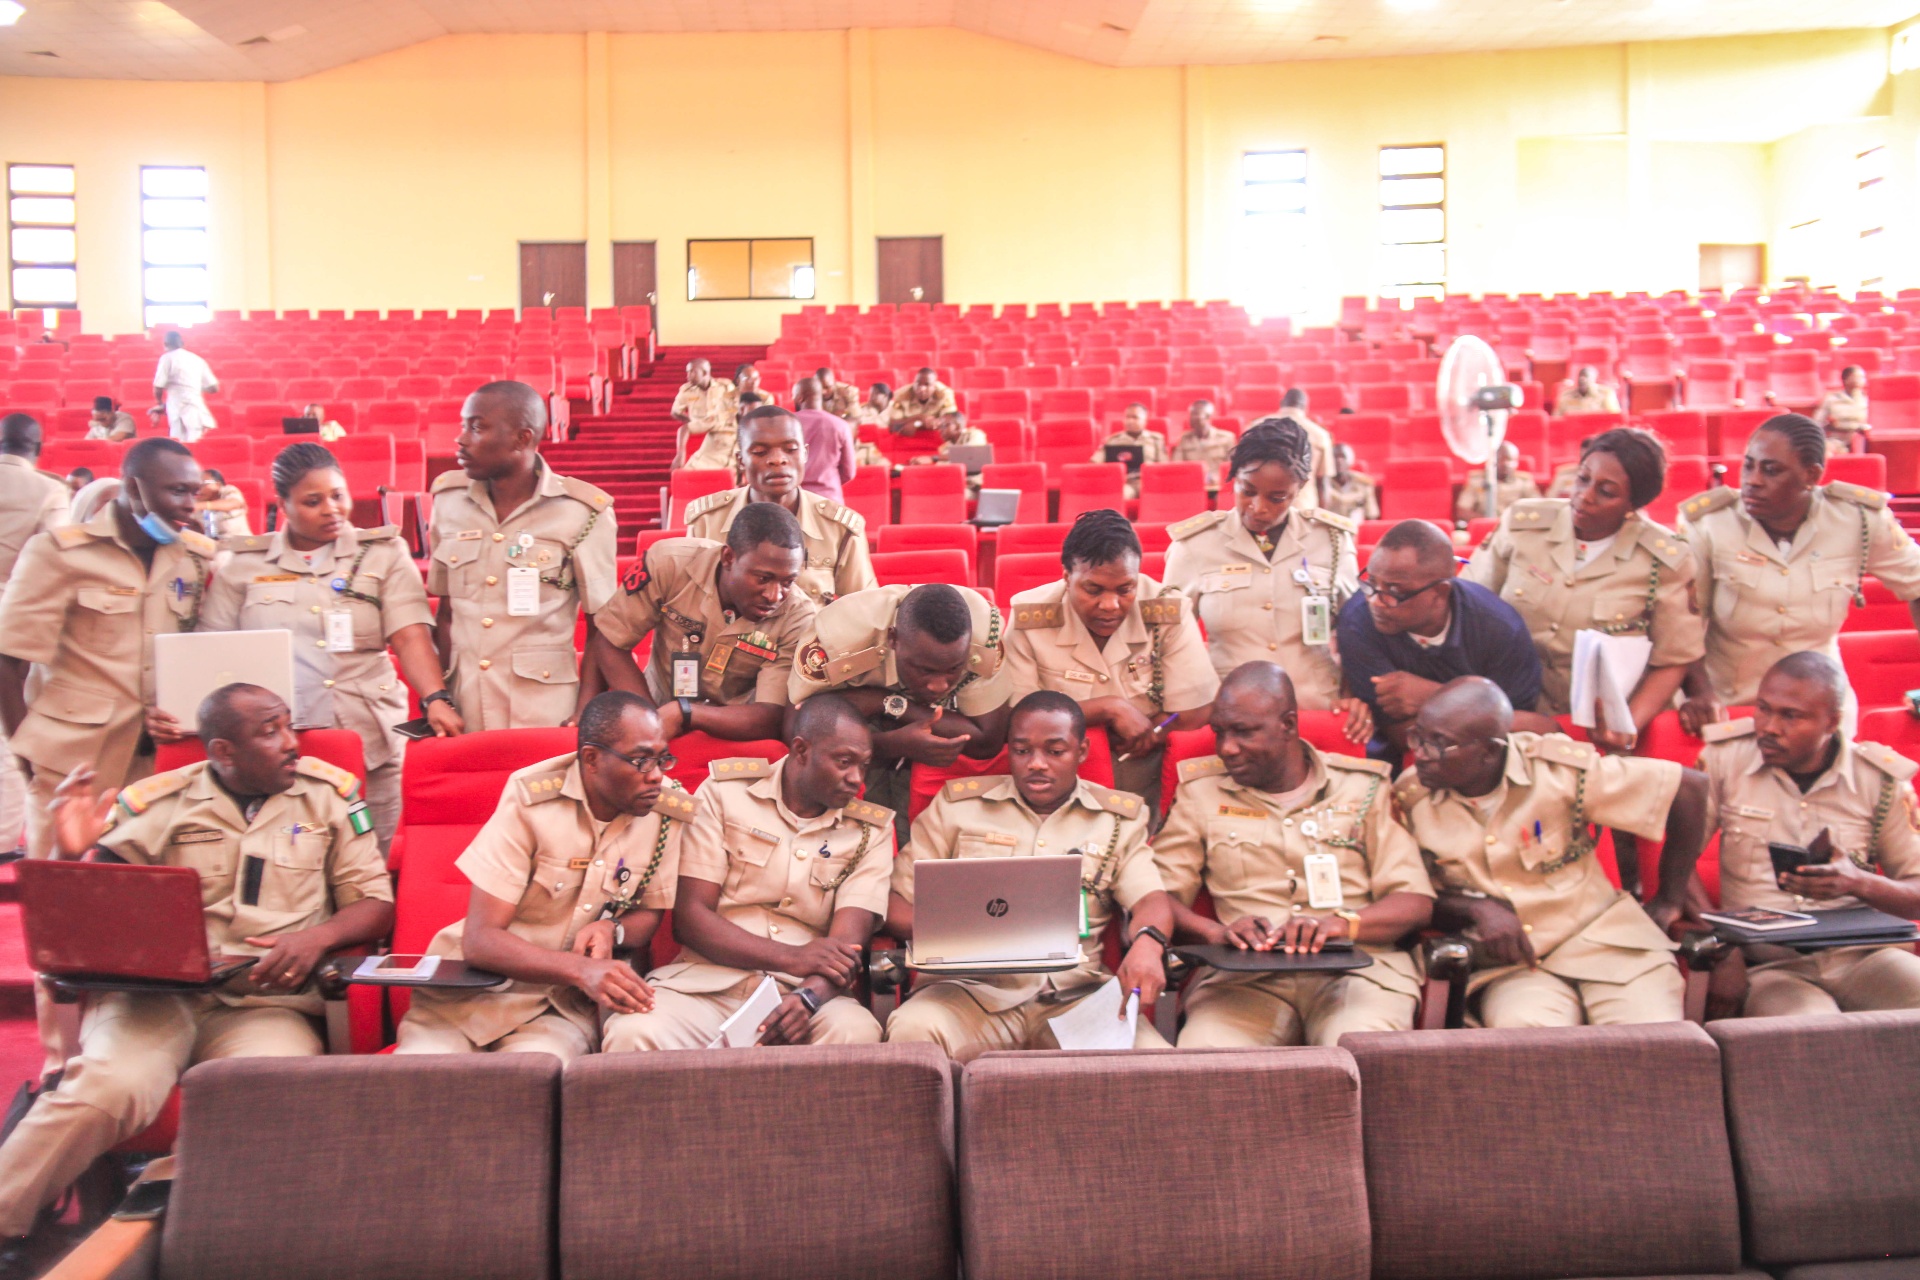
Corporate Workshop
Group training session
Build with AI
Build with AI event group photo
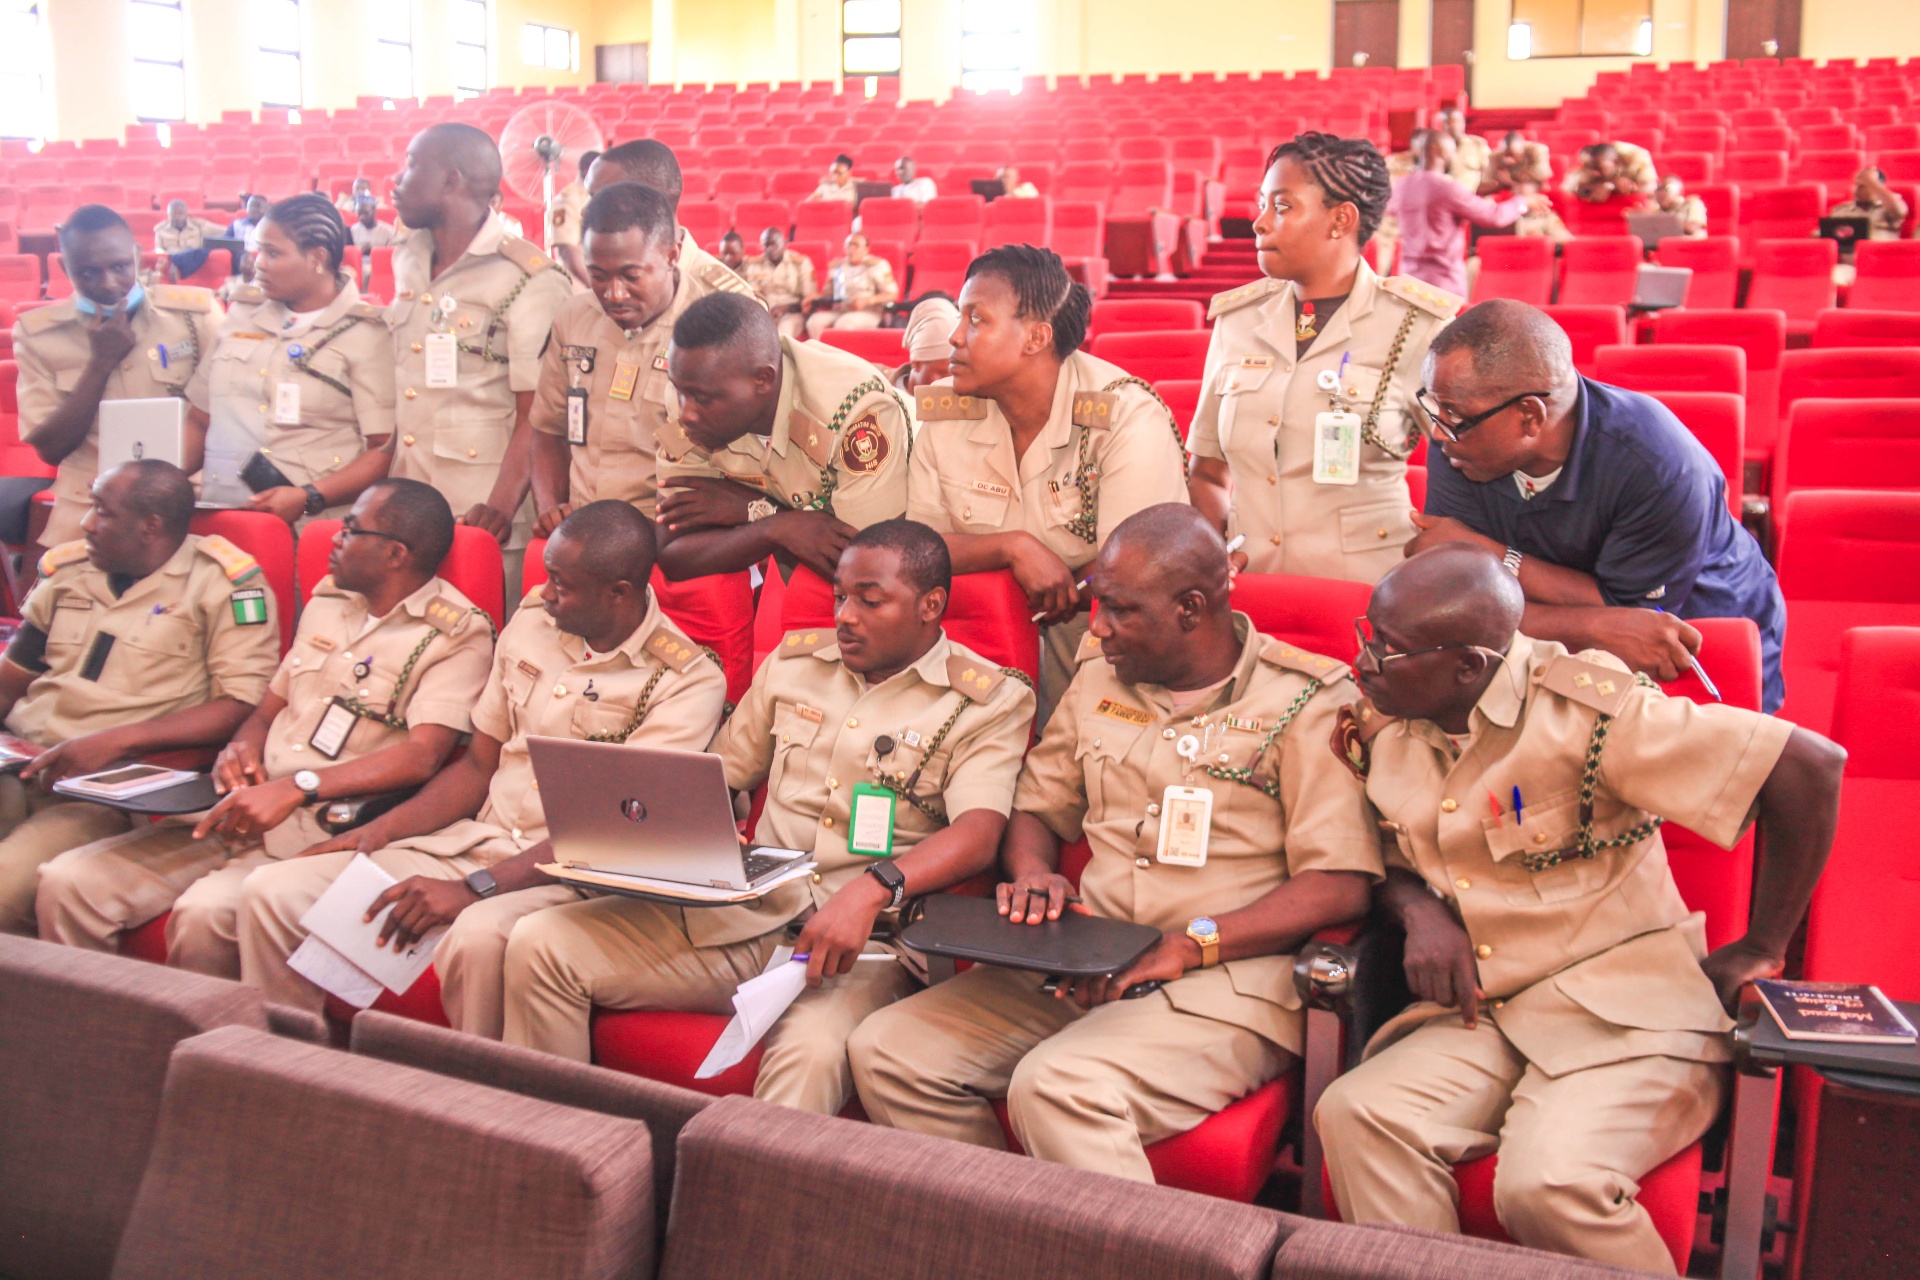
Team Sessions
Team collaboration during workshop
GDG Lagos Event
GDG Lagos Build with AI event
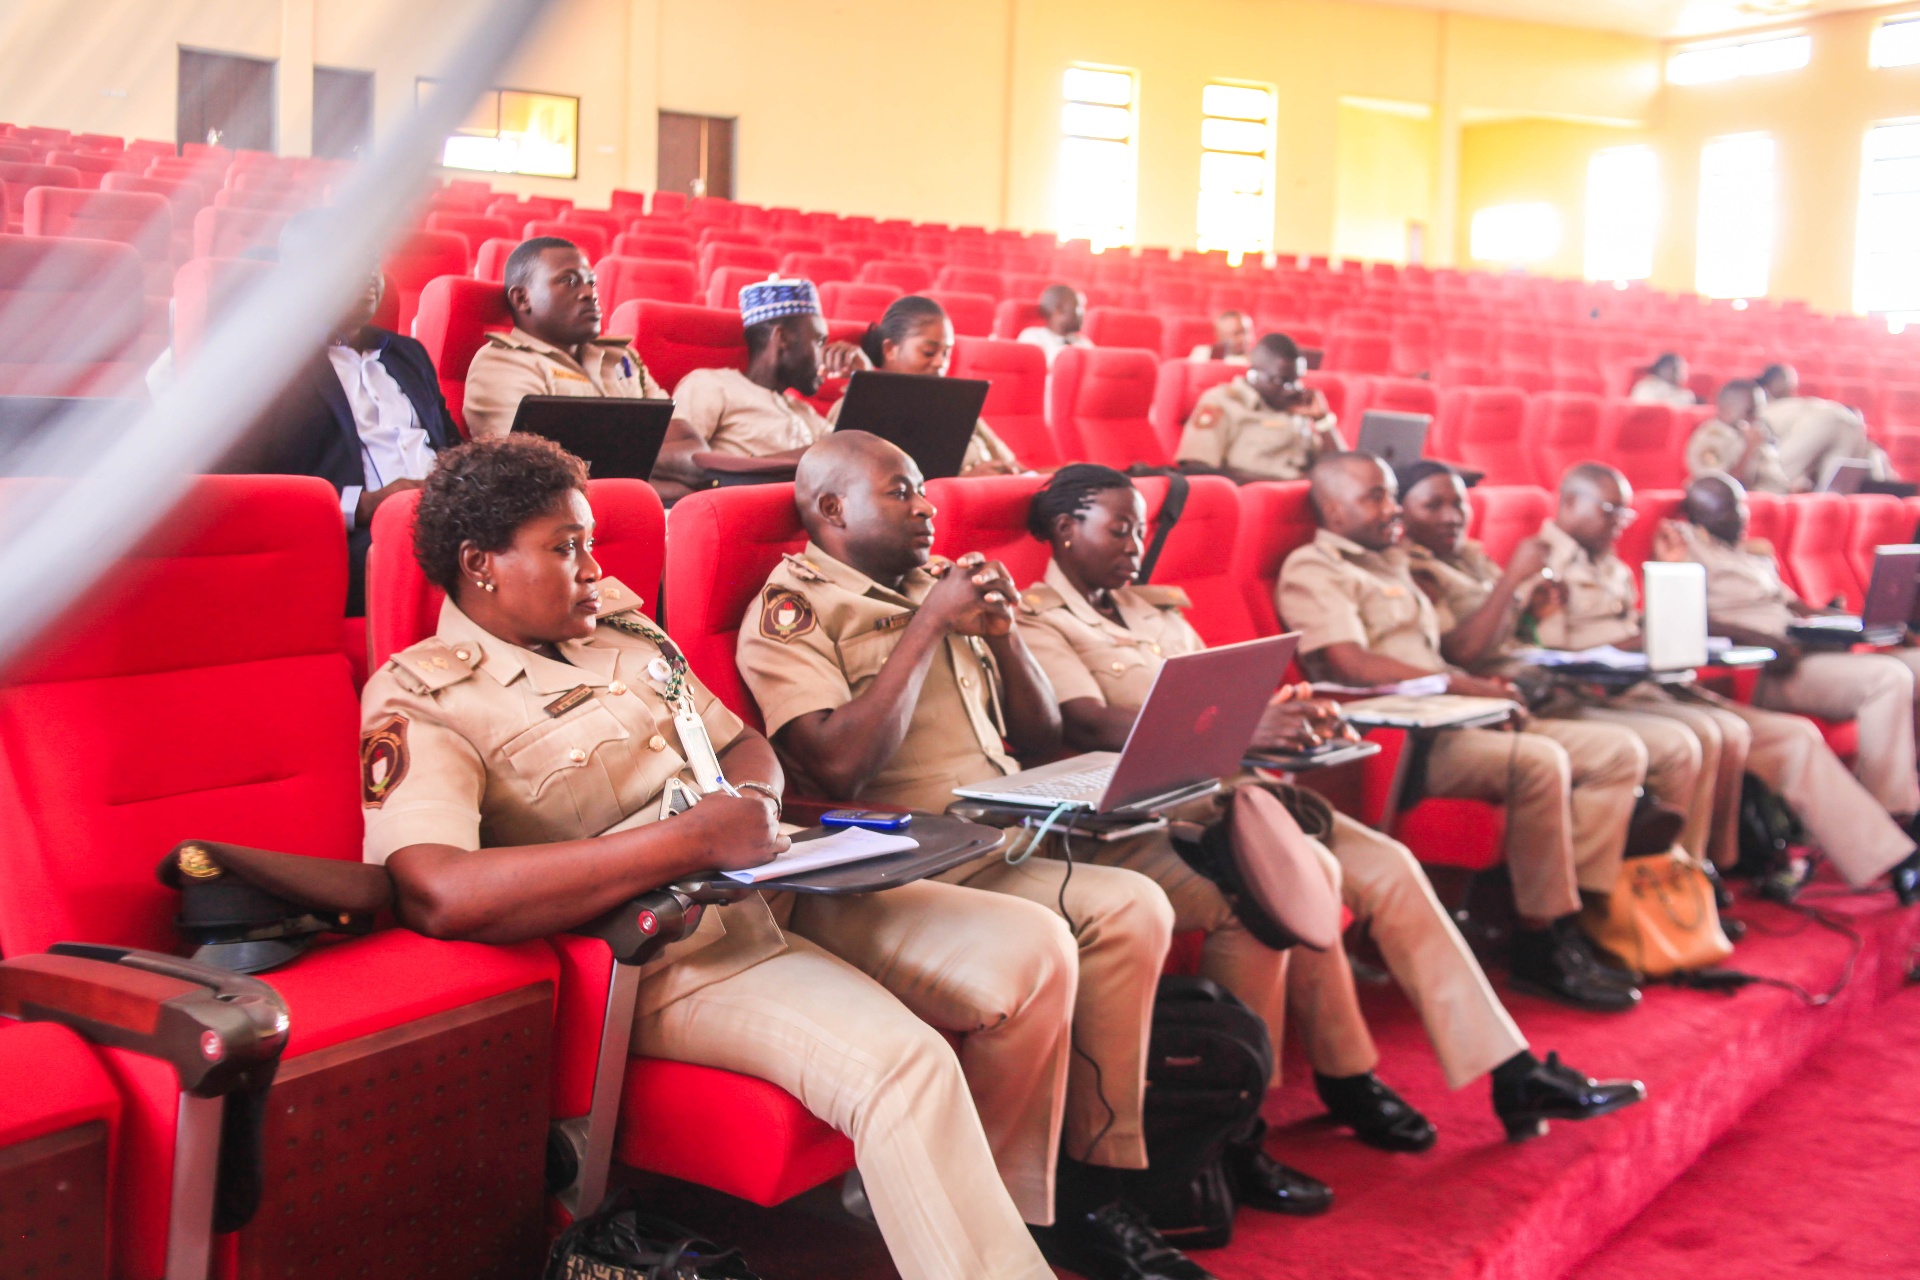
Learning Session
Participants learning during session
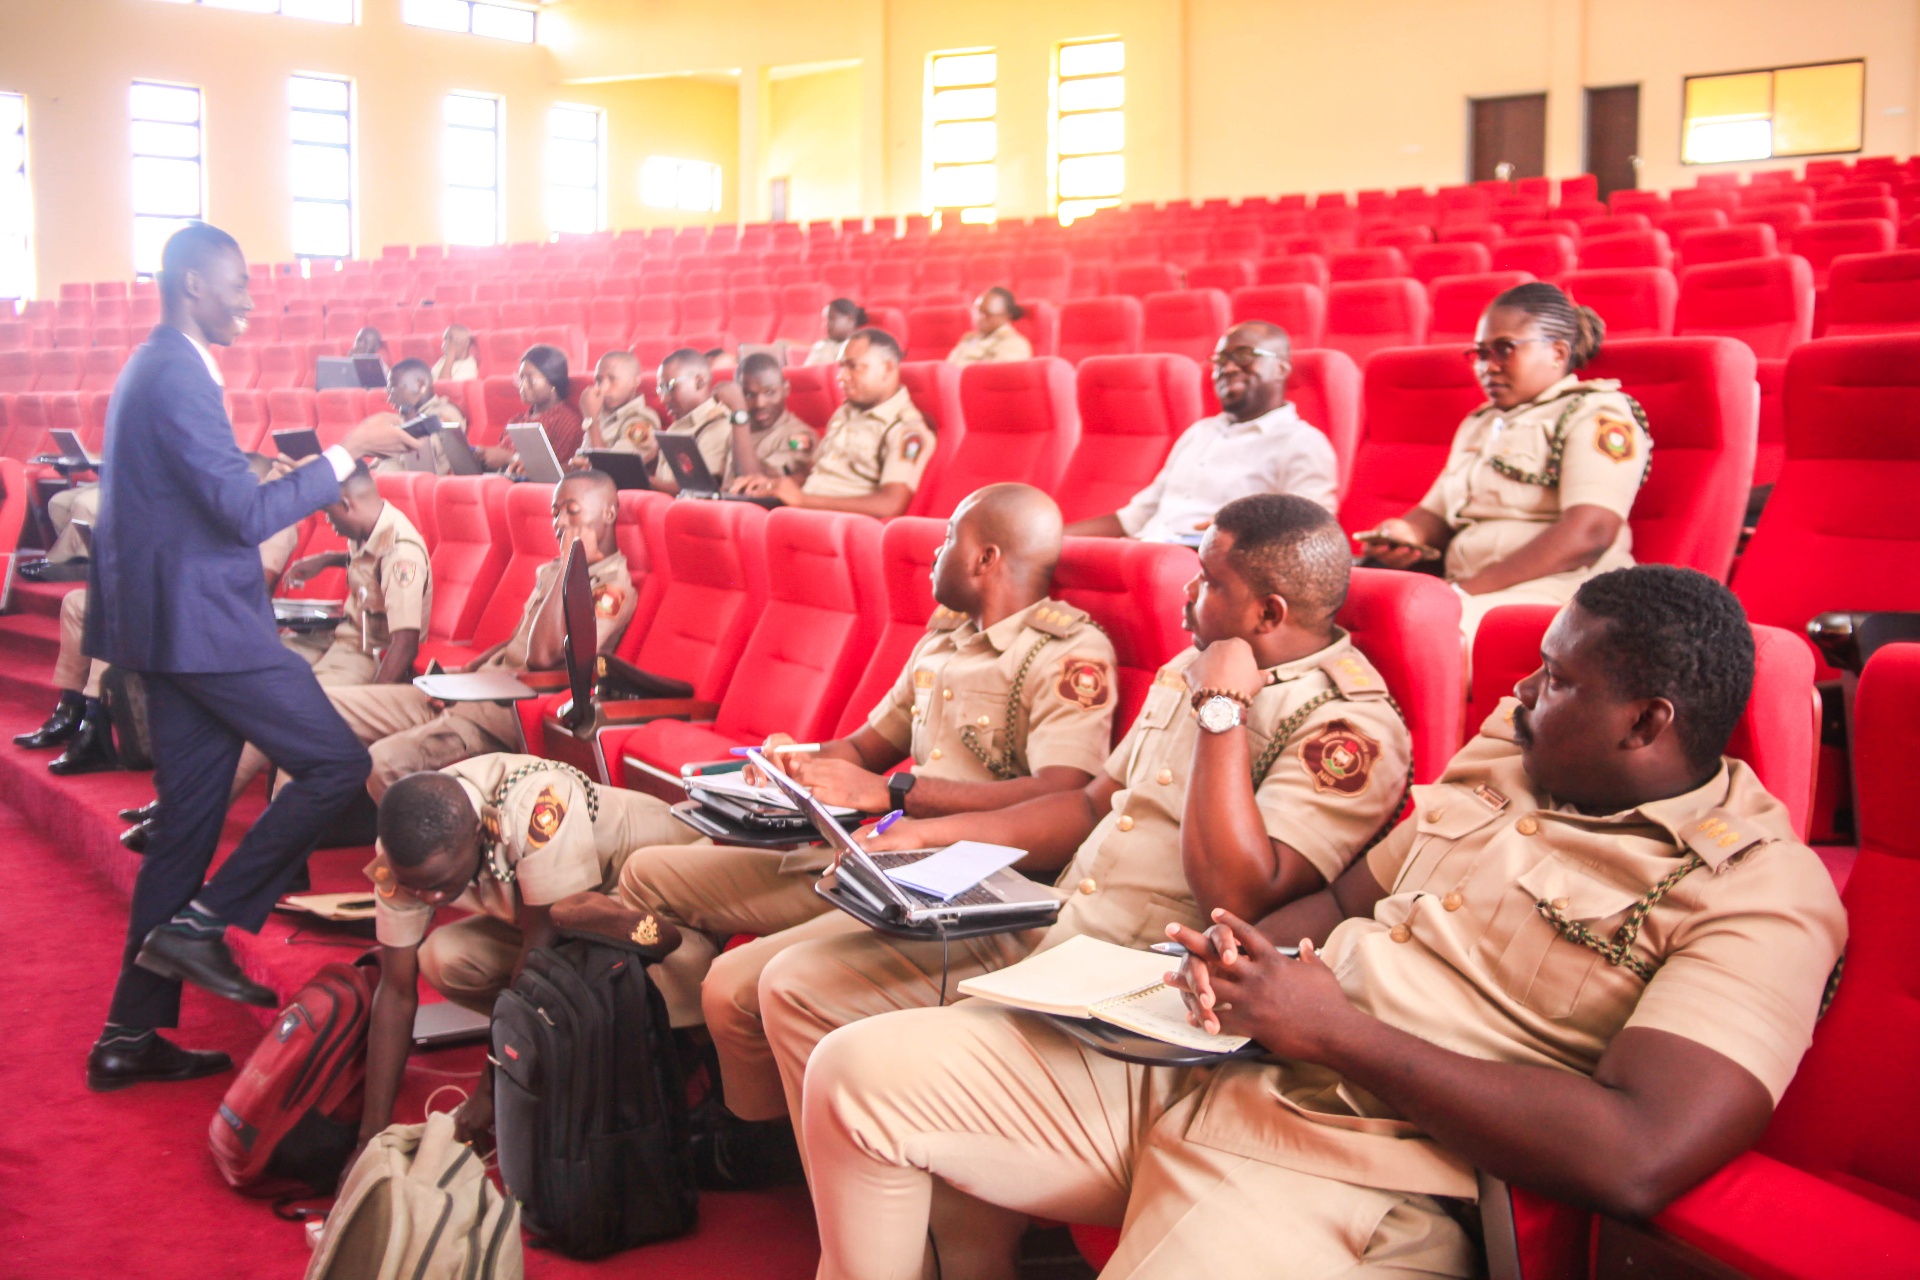
Interactive Workshop
Interactive workshop moment
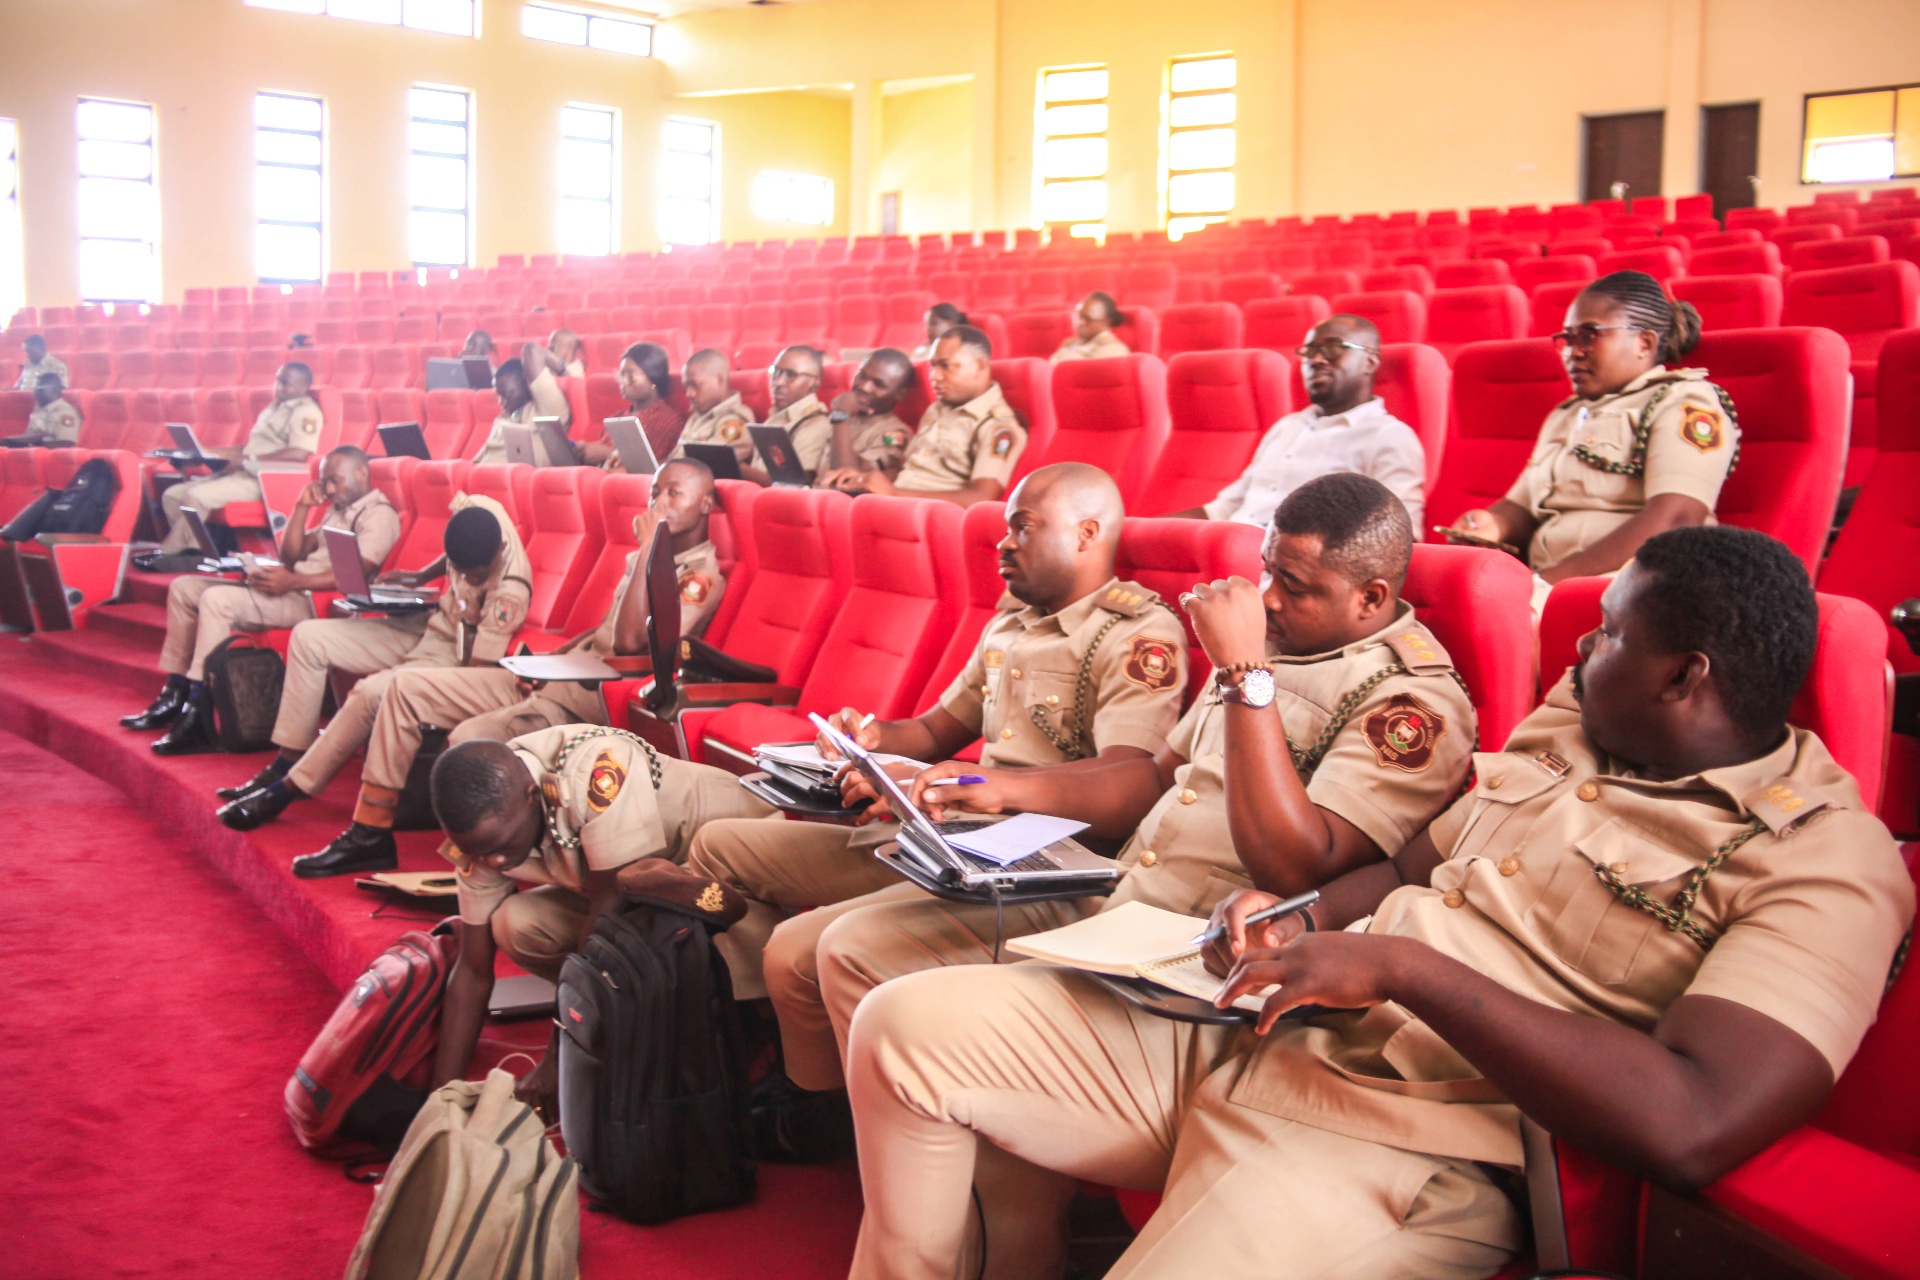
Technical Training
Workshop attendees engaged
I Also Write
My thoughts on technology, security, and where I think the future is heading
Diagnosing Cloud Run Deployments: Build, Revision, IAM and Runtime Failures
Cloud Run incidents are easiest to resolve when the deployment is treated as a chain of independently testable stages. This field guide turns an ambiguous failed deployment into a short sequence of evidence-backed checks.
Engineering Continuous Compliance Evidence for Regulated Health-Tech on GCP
How to turn HIPAA, GDPR and security-control requirements into continuously collected technical evidence instead of a last-minute audit exercise.
A Practical GCP FinOps Audit: From Billing Export to Remediation
A defensible workflow for finding waste, allocating spend, testing recommendations and proving that cloud-cost remediation actually worked.
Securing Mobile Release Pipelines for Google Play and the App Store
Release engineering controls for signing, store credentials, policy checks, provenance and recoverable mobile deployments.
Scheduled Analytics on GCP: Cloud Run Jobs, Scheduler, OIDC and Safe Reporting
A production pattern for scheduled analytics that uses explicit identities, idempotent jobs, observable delivery and minimal secret exposure.
Ways to work together
Consulting, delivery and education services organised around the outcomes teams need most.
Cloud Services
Secure foundations, automated delivery, operational visibility and resilient cloud platforms.
Cloud Security Audit
I run a comprehensive security posture assessment of your GCP or Azure environment — firewall rules, IAM bindings, org policies, and encryption controls — and deliver a prioritised remediation report with exact fix commands.
- VPC firewall & network risk scoring
- IAM privilege and stale-key audit
- Organisation Policy baseline check
- Prioritised HTML remediation report
Zero-Trust Architecture Design
I replace perimeter-based security with identity-first access controls across your entire cloud environment — BeyondCorp access policies, Cloud Armor WAF, VPC Service Controls, and Workload Identity Federation.
- BeyondCorp & Cloud IAP rollout
- Cloud Armor WAF (OWASP CRS)
- VPC Service Controls perimeters
- Workload Identity — no SA keys
Cloud Migration & Modernisation
I plan and execute migrations from legacy infrastructure or Heroku/shared hosting to GCP — workload assessment, migration sequencing, containerisation, and a post-migration reliability review — with minimal downtime and no data loss.
- Workload assessment & sequencing
- Containerisation & Cloud Run setup
- Database migration with zero data loss
- Post-migration reliability review
Cloud FinOps & Cost Optimisation
I audit your GCP or Azure spend, identify waste, and build the infrastructure for ongoing cost visibility — billing exports to BigQuery, anomaly detection, committed use discount analysis, and a real-time Looker Studio dashboard.
- Idle resource detection & cleanup
- Node pool & instance rightsizing
- Committed use discount analysis
- Real-time cost monitoring dashboard
Cloud Observability & Monitoring Setup
I instrument your GCP services with structured logging, distributed tracing, and custom metrics — then build the dashboards and alerts that give your team full visibility into production health before your users notice something is wrong.
- OpenTelemetry instrumentation
- Cloud Monitoring SLO dashboards
- Log-based alert policies
- Looker Studio operational dashboard
SLO Design & Reliability Audit
I define service-level objectives for your production systems, build the alerting infrastructure to enforce them, and design runbooks so your team knows exactly what to do when error budgets burn faster than expected.
- SLO & SLI definition per service
- Error budget burn rate alerting
- Cloud Monitoring dashboard setup
- On-call runbook documentation
DNS, Email & Domain Infrastructure
I provision production-ready DNS and email infrastructure for new domains — MX records, SPF, DKIM, DMARC, CAA records, Cloud Run domain mapping, and TLS certificate automation — fully configured via Cloudflare and GCP APIs in under an hour.
- Cloudflare DNS automation
- SPF, DKIM & DMARC setup
- GCP Certificate Manager (auto-renewal)
- DMARC aggregate report pipeline
CI/CD Pipeline Implementation
I design and implement end-to-end CI/CD pipelines that take your code from commit to production safely — with automated testing, container scanning, and progressive delivery built in from the start.
- GitHub Actions & Cloud Build setup
- Container scanning (Trivy + Snyk)
- GKE / Cloud Run deployment automation
- Canary & blue-green delivery strategies
DevSecOps Integration
I embed security into every stage of your development pipeline — SAST, dependency scanning, container signing, DAST against staging, and infrastructure-as-code validation — so security is never a blocker.
- SAST with Snyk & Semgrep
- Container scanning & Binary Authorization
- OWASP ZAP authenticated DAST
- Checkov IaC security validation
Kubernetes Security Hardening
I harden your GKE environment for production and audit readiness — RBAC least-privilege design, OPA Gatekeeper admission policies, Kyverno enforcement, Falco runtime threat detection, and default-deny network segmentation.
- RBAC & namespace access design
- OPA Gatekeeper & Kyverno policies
- Falco runtime threat detection
- Default-deny NetworkPolicy setup
Infrastructure as Code (Terraform)
I convert manually-created cloud infrastructure into reproducible Terraform code — or build your IaC foundation from scratch — with reusable modules, remote state, and a drift-detection system so your infra never surprises you.
- Terraform module development
- Console-to-code migration
- Remote state & environment separation
- Automated drift detection
Security Incident Response Automation
I build automated incident response systems that contain cloud security threats in minutes — SCC-triggered Cloud Functions that quarantine compromised VMs, revoke suspicious IAM bindings, and notify your team before a human has even opened their laptop.
- SCC finding → automated containment
- 8 incident type response handlers
- PagerDuty & Slack escalation
- Full audit trail to BigQuery
Product Development Services
The product systems, release paths and insight loops that help teams ship with confidence.
App Store & Play Store Programme
I manage the full mobile publishing lifecycle — code signing, automated build and release pipelines with Fastlane, Play Store internal/closed/production track management, TestFlight, crash monitoring, and Google Play Testing Programme enrolment.
- Fastlane Android & iOS automation
- Play Store track & rollout management
- Google Play Testing Programme setup
- Crashlytics monitoring & ANR triage
Product Analytics Infrastructure
I deploy and configure a self-hosted PostHog analytics stack on GCP — keeping all product event data within your own infrastructure — and integrate it with your web and mobile apps for unified behavioural analytics across platforms.
- Self-hosted PostHog on GCP VM
- Flutter & Next.js SDK integration
- Consent-gated initialisation (GDPR)
- BigQuery export for deep analysis
Privacy Policy & App Store Compliance
I write GDPR and NDPA 2023-compliant privacy policies for apps and web products, complete the Google Play Data Safety form and Apple App Privacy Label accurately, and implement cookie consent — resolving the most common cause of store rejections.
- GDPR & NDPA 2023 privacy policy
- Play Store Data Safety form completion
- Apple App Privacy Label mapping
- Cookie consent implementation
Compliance Services
Defensible controls, privacy-aware product practices and practical technical evidence.
HIPAA / ISO 27001 / SOC 2 Compliance
I implement and evidence compliance controls on GCP for HIPAA, ISO 27001:2022, and SOC 2 Type II — from gap assessment through to certification-ready evidence packages that satisfy external auditors.
- Full gap assessment & risk register
- Technical control implementation
- Automated evidence collection
- Certification-ready evidence package
BAA / DPA Audit & Acquisition
I identify every third-party vendor processing your users' data, assess whether a Business Associate Agreement or Data Processing Agreement is in place, flag uncovered gaps, and manage the acquisition process to get you fully covered.
- Third-party vendor data inventory
- BAA & DPA gap identification
- Agreement acquisition management
- HIPAA & GDPR coverage mapping
NDPA 2023 Compliance (Nigeria)
I implement technical compliance under Nigeria's Data Protection Act 2023 — automated data inventory scanning with Cloud DLP, DPIA process, breach notification procedures, and the infrastructure controls that make compliance evidence-able for the NDPC.
- Cloud DLP data inventory scan
- DPIA for high-risk processing
- 72-hour breach notification setup
- NDPC-ready compliance package
Privacy Policy & App Store Compliance
I write GDPR and NDPA 2023-compliant privacy policies for apps and web products, complete the Google Play Data Safety form and Apple App Privacy Label accurately, and implement cookie consent — resolving the most common cause of store rejections.
- GDPR & NDPA 2023 privacy policy
- Play Store Data Safety form completion
- Apple App Privacy Label mapping
- Cookie consent implementation
IAM Access Review & Governance
I conduct quarterly IAM access reviews across your GCP organisation — risk-scoring every binding, routing certification decisions to the right managers, revoking excess access immediately, and producing BigQuery evidence for SOC 2 and ISO 27001 audits.
- Org-wide IAM binding risk scoring
- Manager-routed certification workflow
- Immediate revocation on approval
- SOC 2 / ISO 27001 evidence package
Disaster Recovery & Backup Verification
I design and automate your disaster recovery programme — Cloud SQL restore testing, audit log integrity verification, backup retention policy enforcement, and runbook documentation — so your backups are proven restorable before you need them.
- Automated monthly restore testing
- Cryptographic audit log integrity
- Retention Lock policy enforcement
- DR runbook documentation
Education Services
Hands-on programmes that leave teams more capable than they arrived.
Technical Training & Enablement
I design hands-on technical training for teams that need to operate securely and independently — from cloud and Linux foundations to compliance-aware administration and DevOps delivery practices.
- Role-based learning plans
- Hands-on cloud and Linux labs
- Compliance-aware administration training
- Operational runbooks and knowledge transfer
Let's build something extraordinary together
If you want to transform your cloud infrastructure, harden your systems, or weave AI into what you already run — I'd love to help.